Is your Kubernetes API Server exposed?
This article was originally published on Medium.
After reading “Over 380 000 open Kubernetes API servers”, I wondered whether some of the clusters I manage could be exposed. I decided to check, and I think you should too!
What are we talking about?
If you work with Kubernetes, there is a good chance that most of your interactions with it go through the Kubernetes API Server. Almost every time you use kubectl, k9s, Lens or Octant, you are in fact sending HTTP requests to the API Server.
What matters here is:
- Where are you talking to the API from?
- And what’s in between?
If you are using your Kubernetes client through a bastion host and/or a virtual private network (VPN), you are probably in a good spot. If not, or if in doubt, you should definitely check!
Why would it be exposed?
There could be many different answers to this question, but the most common one is probably: because it’s the default!
I’m going to use Amazon Elastic Kubernetes Service (EKS) as an example here. When you create an EKS cluster on AWS, here’s what you will find by default on Step 2 “Specify networking”:
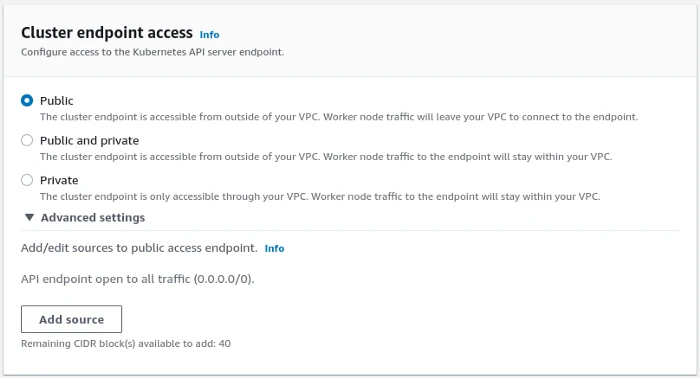
This means that all clusters created using the default configuration expose the API Server to the entire internet (0.0.0.0/0)! A bit scary… but let’s not panic!
How to test?
To test your cluster configuration, you will need the IP or FQDN of your Kubernetes API Server(s). In most cases, you will find this information in your Kubernetes configuration file:
$ grep server ~/.kube/config
server:https://XXXXXXXXX.abc.us-west-1.eks.amazonaws.com
server:https://XXXXXXXXX.abc.us-west-1.eks.amazonaws.com
server:https://XXXXXXXXX.abc.us-west-1.eks.amazonaws.com
Once you have this, you can simply try to query the /version endpoint from your terminal or any web browser:
$ curl -k https://XXXXXXXXX.abc.us-west-1.eks.amazonaws.com/version
{
  "major": "1",
  "minor": "20+",
  "gitVersion": "v1.20.15-eks-a64ea69",
  "gitCommit": "03450cdabfc4162d4e447e6d8c5037efe6d29742",
  "gitTreeState": "clean",
  "buildDate": "2022-05-12T18:44:04Z",
  "goVersion": "go1.15.15",
  "compiler": "gc",
  "platform": "linux/amd64"
}
If you get a similar answer, it means that your Kubernetes API Server is exposed on the internet.
How to fix it?
There are many ways to fix this. I will share a quick way to reduce the attack surface, and also recommend a better architecture.
The quick fix
This one is straightforward and you should be able to apply it immediately in your AWS console.
- For a new cluster: EKS > Clusters > Create EKS cluster > Specify networking
- For an existing cluster: EKS > Clusters > ${Your-Cluster} > Networking Tab > Manage networking
Once there, unfold Advanced settings and you will be able to add up to 40 source CIDR blocks. If you want to allow a single IP address, just append /32 to it, like this:
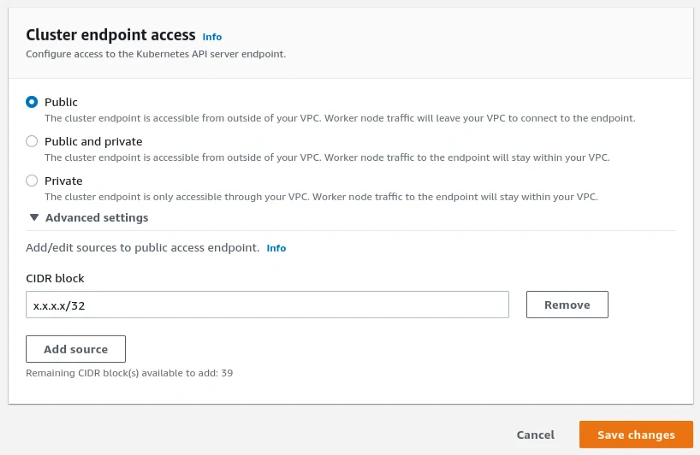
With this solution, your Kubernetes API server is still publicly exposed on the internet, but only the configured CIDR blocks will be allowed to access it.
To get your public IP, you can use a service like whatismyip.com or use dig:
$ dig +short [email protected]
x.x.x.x
A better approach
Once you have limited your public exposure, you have time to think and work on a more secure and sophisticated architecture to manage your Kubernetes cluster(s).
I personally recommend the following:
- Use a VPN to access your Virtual Private Cloud (VPC)
- Configure your EKS Cluster endpoint access to Private mode
- Create a private SSH bastion host in your VPC
- Update your EKS Security Group to only allow inbound traffic from the bastion host
- Enable access & audit logs on your bastion
Here’s what the architecture looks like:
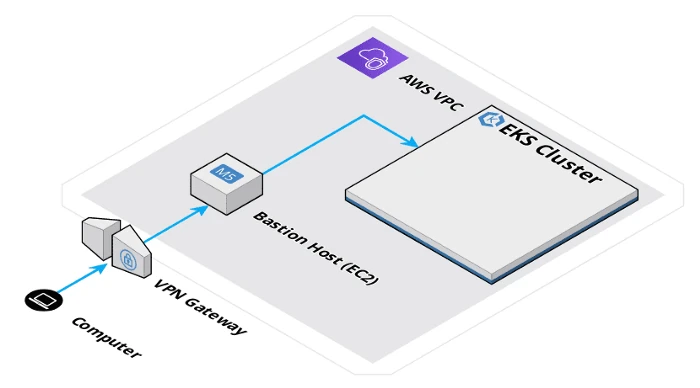
While this article uses AWS as an example, you should be able to reproduce something similar on most cloud providers.
Final words
Checking whether your API Server is exposed only takes a curl, and the quick fix only takes a few minutes in the AWS console. If your clusters are still open to 0.0.0.0/0, start there today, then plan the move to a private endpoint behind a VPN and a bastion host.
Feel free to send me feedback if you find any errors or think of any improvements!